[ 04 // OPERATIONS ]
active builds
// op_001
 CyberCore Academy
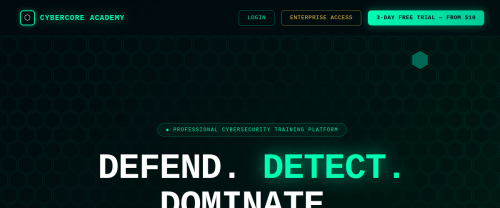
Cybersecurity awareness training SaaS built on React 19 and a Node/Express backend with better-sqlite3, deployed on Railway. Features 77 training modules across 12 domains, 46 earnable badges, and a decision-tree simulation engine that branches dynamically on user choices inside real-world attack scenarios — phishing, social engineering, insider threat, and physical security. XP and leveling are a fully decoupled scoring engine so badge logic and training content evolve independently without touching each other's code. Full admin panel with cohort management, per-user progress tracking, and completion reporting. Stripe-powered subscription billing with webhook-driven lifecycle management and a complete audit trail. Enterprise edition maps completions to SOC 2, NIST CSF, and HIPAA controls — turning training records into audit-ready compliance evidence.
React 19
Node
SQLite
Stripe
Railway
LIVE
// op_002
 Vitality
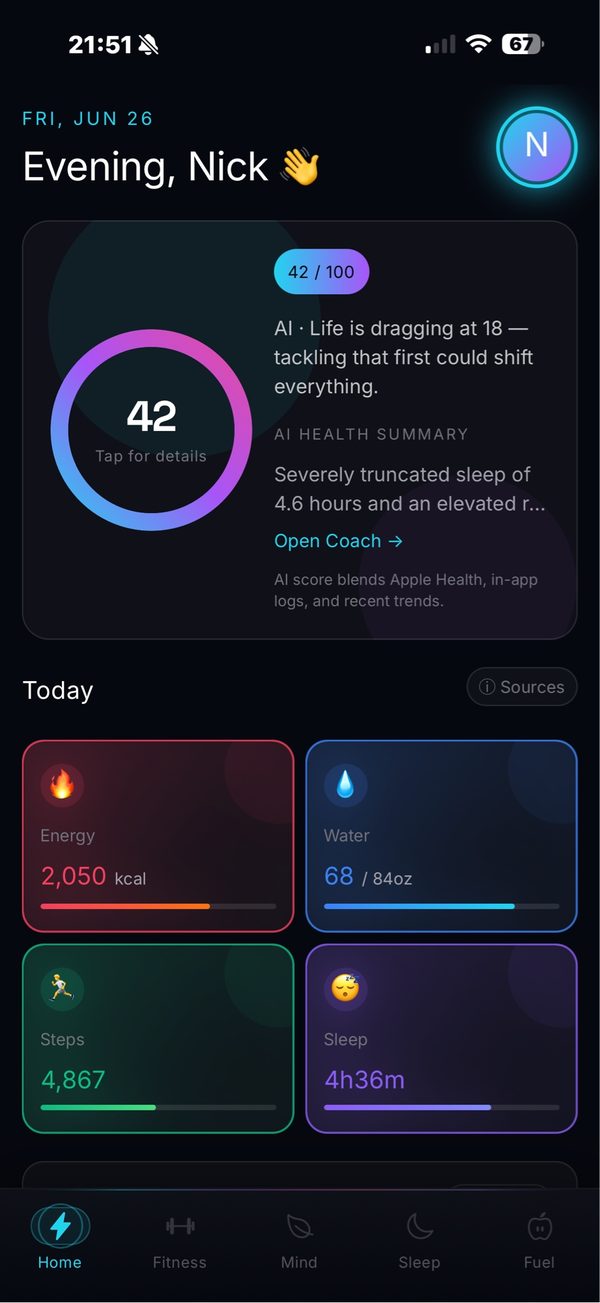
All-in-one iOS wellness platform built with Expo Router and TypeScript, tracking five health pillars — fitness, sleep, nutrition, mental health, and life habits — and synthesizing them into a unified daily wellness score. AI Wellness Coach is powered by Claude via a Node/Express backend on Railway, reading cross-pillar logged data to produce personalized guidance grounded in the user's actual history rather than generic recommendations. GPS workout tracking runs as a background location service recording full route geometry via expo-location. AI meal scanning uses the device camera to estimate calories and macros in real time. HealthKit integration reads and writes steps, heart rate, sleep, and workout data bidirectionally. Zustand manages client-side state. Free tier covers basic tracking; $19.99/month Premium unlocks the AI Coach, deep cross-pillar trend insights, personalized daily plans, and meal photo scanning. Now live on the App Store.
React Native
Expo
TypeScript
Zustand
LIVE
// op_003
Terminal Connection
Three-component architecture for remote Kali Linux terminal access from an iOS or Android device. The Python PTY server spawns a pseudo-terminal on the host using pty.spawn, piping stdin and stdout bidirectionally over a WebSocket connection. A Node.js/Socket.io relay broker sits between the host and client, handling session multiplexing and message routing so the host never exposes a direct public socket. The React Native client embeds xterm.js inside a WebView with a custom virtual keyboard overlay optimized for terminal input on mobile. Auth is token-based with short-lived signed tokens — no hardcoded credentials anywhere in the chain. The relay handles reconnection logic and session keepalives so dropped connections resume cleanly without losing terminal state.
Python
Socket.io
React Native
xterm.js
LIVE
// op_004
CyberCore Mobile
Native iOS companion app for CyberCore Academy built with React Native and Expo, sharing the same Node/SQLite backend via JWT authentication. Apple Sign-In handles identity with tokens stored in the iOS Keychain and Face ID biometric re-authentication on app resume. RevenueCat manages in-app subscription state and App Store receipt validation, keeping billing logic fully out of the app and synced against the backend user record. Push notifications delivered via APNs with Expo's notification service as the abstraction layer. App Store builds are fully automated through Codemagic CI — code signing, provisioning profiles, versioning, and binary submission handled in the pipeline with zero manual Xcode steps required.
React Native
Expo
RevenueCat
JWT
LIVE
// op_005
SiemLess
Self-hosted SIEM built with async FastAPI, PostgreSQL for structured event storage with full-text search, and Redis as a pub/sub layer that fully decouples alert delivery from the ingestion pipeline so high-volume ingest never blocks alerting. Ingests via Syslog UDP/TCP on port 514, a REST HTTP API, a batch endpoint accepting up to 1,000 events per request, and file upload. Parser layer handles SSH auth logs, Apache/Nginx access logs, iptables firewall events, sudo audit records, Windows Security event logs, CEF, syslog RFC3164/5424, and raw JSON. Detection engine runs YAML-based correlation rules — analysts write and version-control detections as plain files with no Python required. Rule types include threshold detection and sliding-window time correlation covering SSH brute force, port scan sequences, privilege escalation chains, and C2 beacon patterns. Threat intel enrichment queries AbuseIPDB and VirusTotal per IP and hash on ingest. Alerting dispatches to SMTP, Slack webhooks, and arbitrary HTTP endpoints in real time. React frontend delivers an event timeline, severity distribution charts, top-sources breakdown, and full-text search with structured filter syntax. Fully Dockerized with Docker Compose for single-command self-hosted deployment.
Python
FastAPI
React
PostgreSQL
Redis
Docker
OPEN SOURCE
// op_006
 VibeMaps
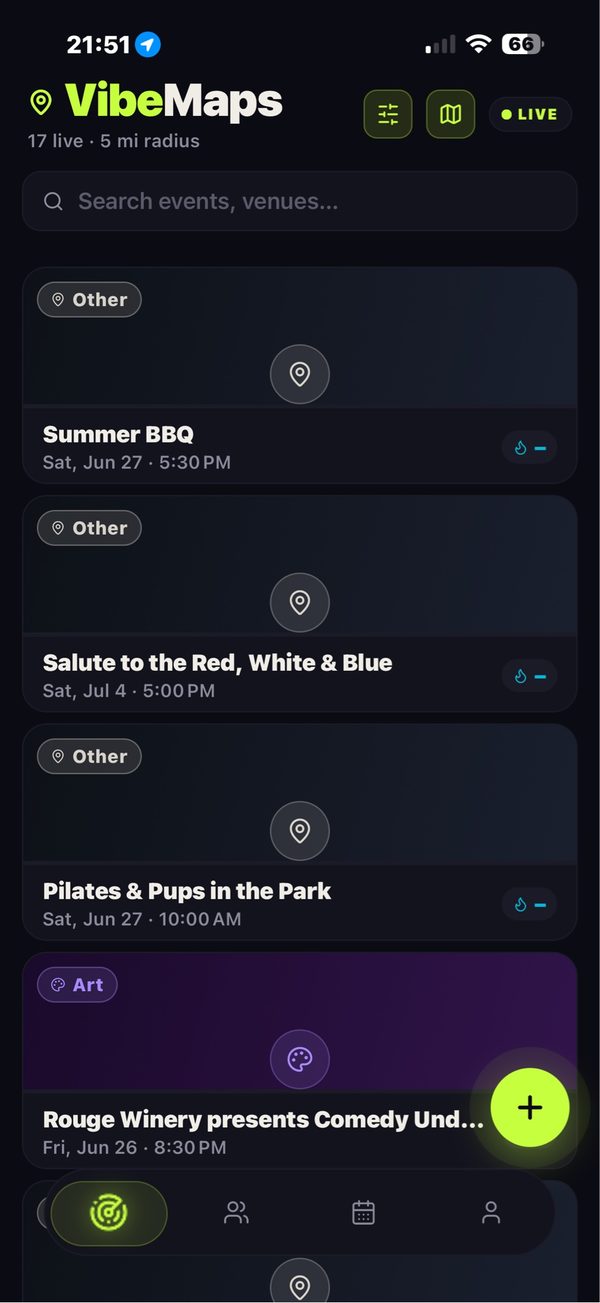
Hyper-local event discovery platform for independent venues — dive bar trivia nights, indie theaters, underground shows, and live music found within a configurable proximity radius. Built on React Native with Expo Router and a Node 22/TypeScript backend backed by PostgreSQL with the PostGIS extension. Geospatial radius queries use ST_DWithin against GIST-indexed geography columns for sub-millisecond proximity filtering. Event data is community-submitted with moderator review — no algorithmic curation, no corporate API scraping, no sponsored placements. Expo push notifications deliver proximity-based alerts without opt-in to any platform interest graph. Deep linking via
vibecheck://event/:id routes directly to event detail screens from any external surface. Discovery is purely radius and community trust.
React Native
Expo
Node 22
PostgreSQL
PostGIS
TypeScript
LIVE
// op_007
 Tattoo Aftercare
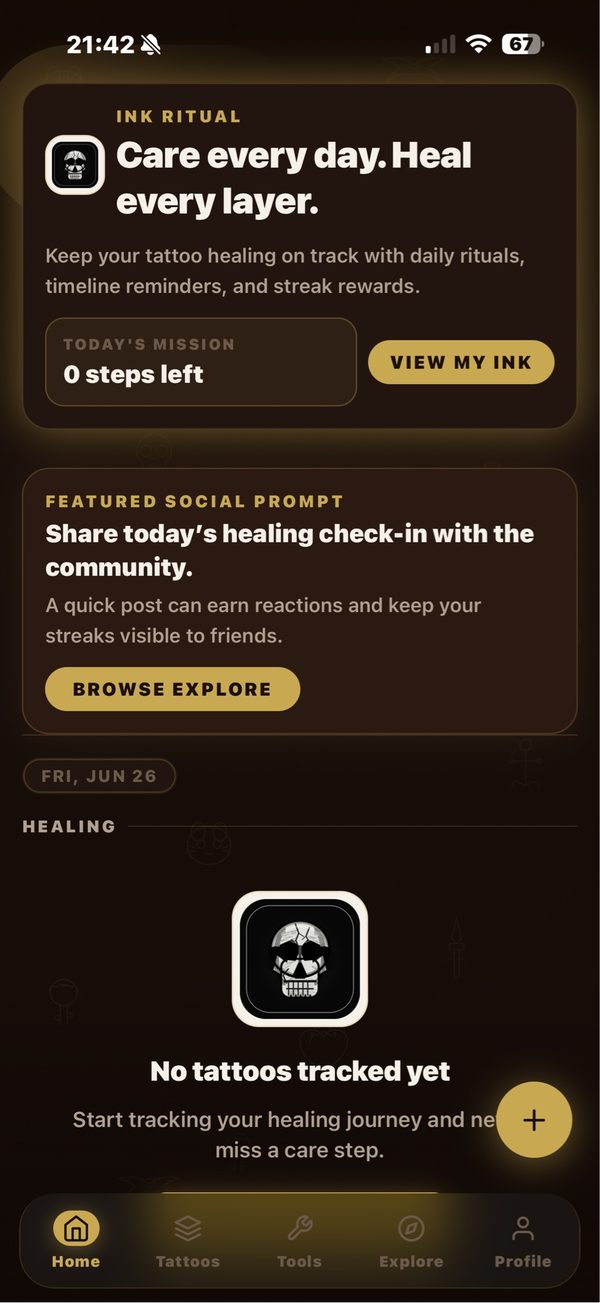
iOS tattoo healing tracker built with React Native and Expo, using expo-sqlite for fully local on-device data storage — no account required, no personal data leaves the device by default. Manages multiple tattoos simultaneously, each with its own healing timeline, stage-based care schedule, and progress photo journal backed by expo-image-picker and expo-media-library with photo metadata stored alongside SQLite records. Smart care reminders are scheduled via expo-notifications against each tattoo's active healing stage and last-logged care action, adapting frequency automatically as the tattoo progresses from fresh wound through fully healed. Apple Sign-In handles optional account creation for community features. RevenueCat manages the one-time $3.99 Pro IAP with App Store receipt validation and entitlement syncing. Community social feed allows users to share healed results and care logs with other collectors. Cloudflare Workers serves the marketing site and admin panel. Now live on the App Store.
React Native
Expo
SQLite
RevenueCat
LIVE
// op_008
 CyberLab Mobile
Professional iOS app for managing a personal cybersecurity lab remotely — the device never runs tools directly, it connects securely over HTTPS + JWT to a private Kali Linux or Ubuntu server where approved tools run inside isolated Docker containers. 14-phase build (Phases 1–13 complete) covering target management, port scanning, network topology mapping with SwiftUI Canvas, web assessment (WhatWeb, Nikto, Nuclei, OWASP ZAP, Gobuster, testssl.sh), OSINT tools (Shodan, VirusTotal, AbuseIPDB, HIBP, IPinfo, WHOIS), vulnerability intelligence with NVD and CISA KEV enrichment, context-aware AI assistant powered by Claude, APNs push notifications with cron-scheduled scans, multi-page PDF report generation, scan diffing, offline SwiftData cache, CVSS v3.1 calculator, WidgetKit extensions, and iOS Shortcuts integration. Face ID unlock, per-target authorization enforcement, full audit trail. Backend is Node.js/TypeScript Express on Railway with PostgreSQL, Drizzle ORM, Redis, Zod validation, and a Python Celery worker queue managing Docker-isolated scanner containers (nmap, masscan, Nuclei, Nikto, OWASP ZAP, testssl.sh, Amass, Subfinder, theHarvester, WhatWeb, Gobuster, dig, whois, arp-scan).
Swift / SwiftUI
SwiftData
Node.js / TypeScript
PostgreSQL
Drizzle ORM
Redis
Docker
Python / Celery
IN DEV
// op_009
 Shield AI
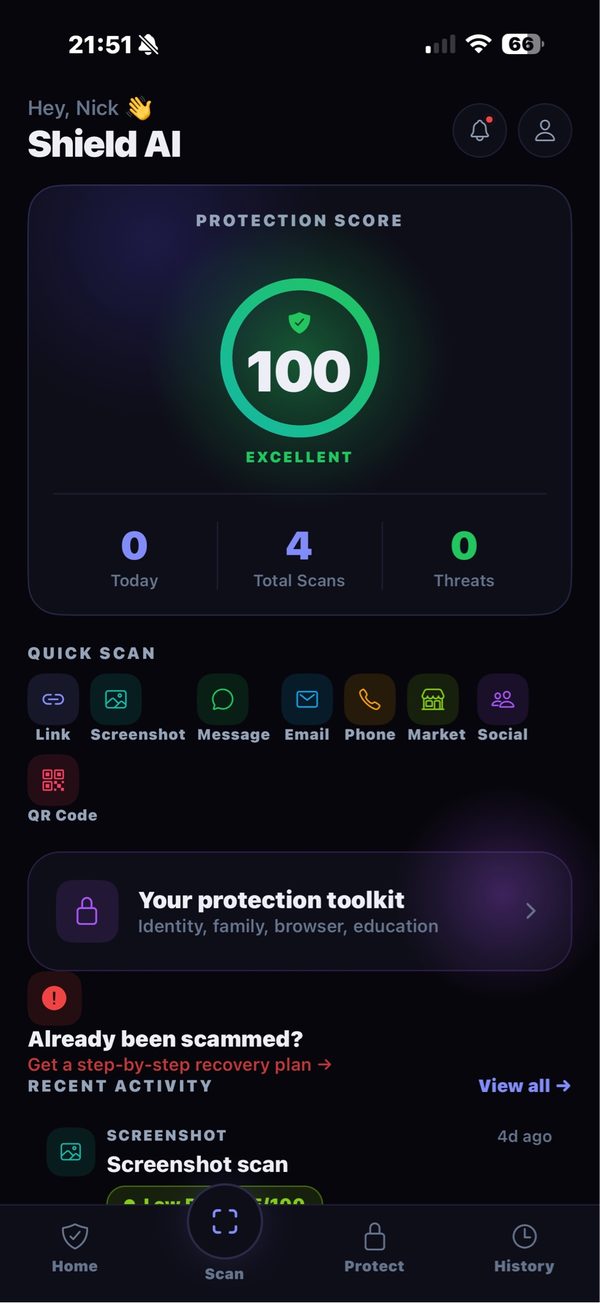
AI-powered scam, fraud, and identity protection assistant built with React Native, Expo, and FastAPI. The core premise: send us anything suspicious — a screenshot, link, or pasted text — and get back a risk score, threat class, plain-English explanation, and exact next steps before you click, pay, or trust. Phase 1 MVP covers screenshot OCR + brand/entity detection, URL scanning via Safe Browsing + WHOIS enrichment, and a structured AI report engine backed by Claude. Detection is layered: deterministic rule checks run first (suspicious TLDs, URL shorteners, brand mismatches, credential prompts), then LLM analysis interprets the evidence — no single point of failure. Async analysis queue (Redis + Celery) keeps mobile response fast. Auth, dashboard, scan history, and a feedback loop for continuous scoring improvement are all in scope for the first release. Roadmap expands to QR scanning, message and email analysis, phone reputation lookup, iOS/Android share extensions, identity breach monitoring, and a guided scam-recovery wizard.
React Native
Expo
TypeScript
FastAPI
PostgreSQL
Redis
Celery
Claude AI
Safe Browsing API
Docker
IN DEV
// op_010
 FileTrail
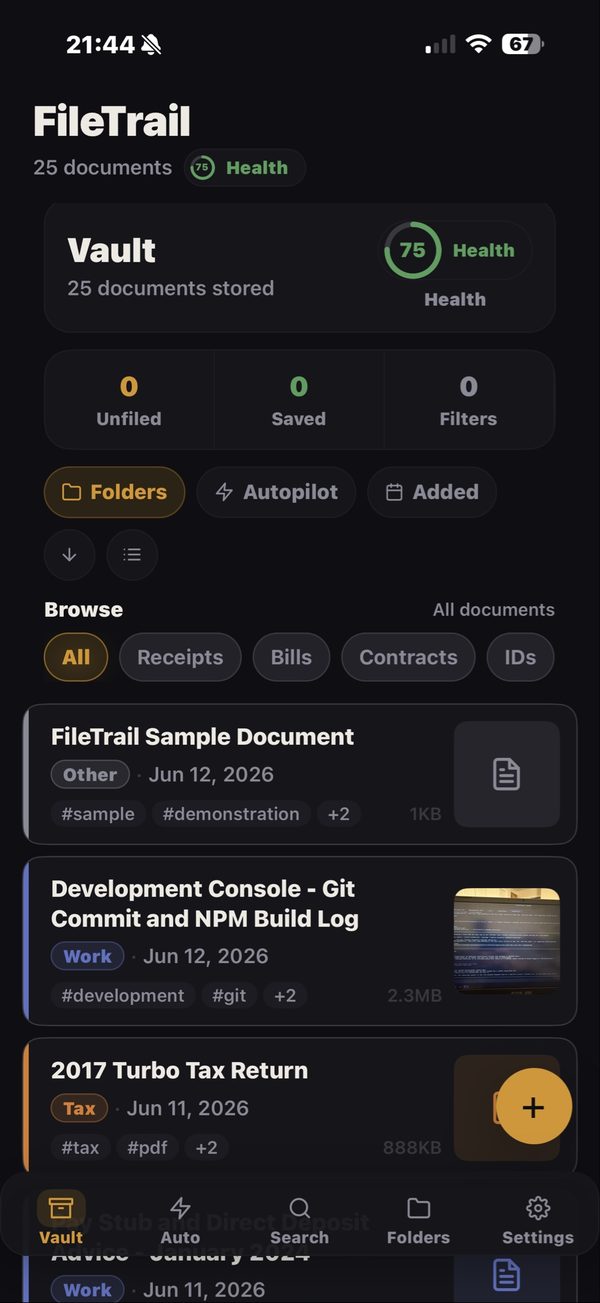
Personal document vault for iOS. Capture documents with the camera, extract text with iOS Vision OCR, and automatically organize everything with a Claude-powered classification engine. A Face ID-protected vault keeps sensitive files private while nested folders, smart renaming, and bulk organize tools keep the workflow fast. RevenueCat handles the Pro subscription for unlimited storage, AI categorization, and cloud backup. The backend runs on Node.js/Express with PostgreSQL and Drizzle ORM, with OpenAPI keeping the mobile client and server aligned.
React Native
Expo
TypeScript
Node.js
PostgreSQL
Drizzle ORM
Claude AI
RevenueCat
IN DEV
// op_011
 Strength In Order
Brand and storefront site for AEGIS Apparel, built to carry the Strength in Order identity through a clean, mobile-first presentation. The layout leans on bold editorial typography, high-contrast imagery, and a direct path from landing page to purchase intent so the brand message stays front and center. The site is a fast React build with lightweight analytics and SEO-minded structure for launch traffic and social sharing.
React
SEO
Responsive UI
Sentry
LIVE
// op_012
 The Sugar Haus Bakery
Custom order and booking platform for a bakery business, built on Node/Express with PostgreSQL. Customers submit custom treat requests through an order form that validates the requested event date against a configurable prep window, checking it against already-accepted orders and manually blocked vacation ranges stored in Postgres. Resend handles transactional email — an instant order-received confirmation to the customer, plus a notification to the baker with an embedded accept/decline link that updates order status without needing to log into the admin panel. Token-protected admin routes manage the order pipeline and date blocks. Sentry covers error monitoring. Deployed on Railway via Nixpacks.
Node.js
Express
PostgreSQL
Resend
Railway
LIVE
// op_013
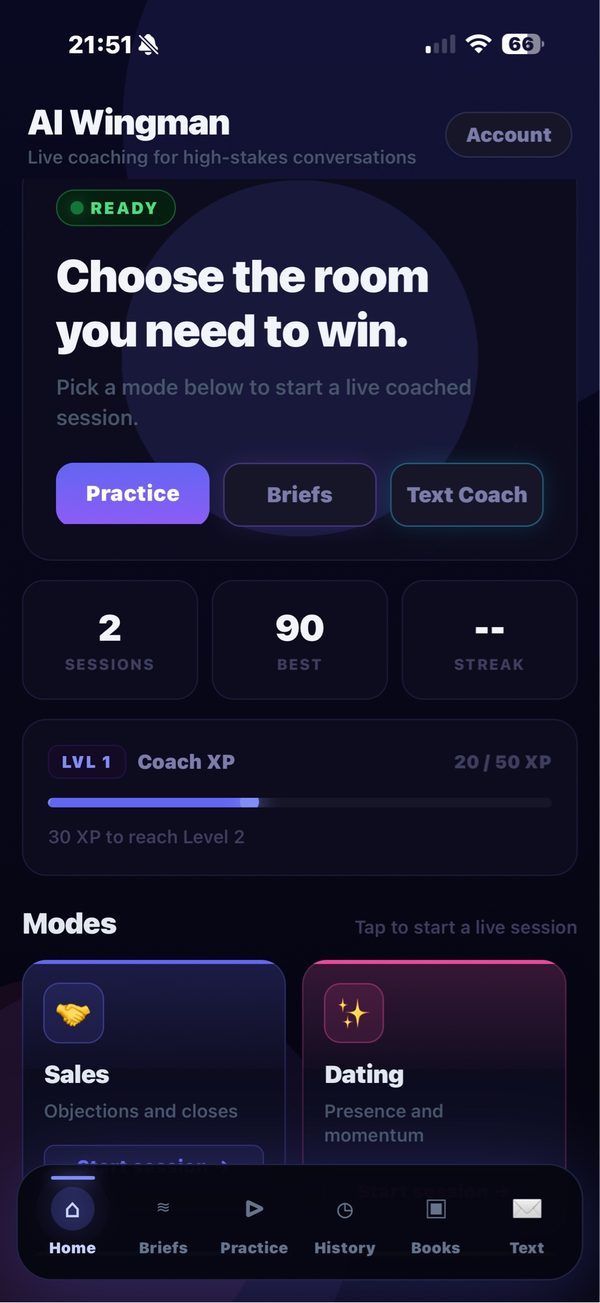 AI Wingman
Live conversation coach for high-stakes moments — sales calls, dates, networking, pitches, and hard conversations. It listens in real time, thinks fast, and whispers the next move through your AirPods, then turns the conversation into recaps, transcript memory, and follow-up actions. Built as a React Native + Expo iOS app with Zustand state and RevenueCat membership, backed by a Node/Express server that streams live transcription via Deepgram and runs coaching through Claude over a WebSocket connection, with PostgreSQL persistence and JWT auth. Organized around a simple loop — prepare, talk, review, follow up, improve — with dedicated Briefs, Practice (voice roleplay with Claude), History, Playbooks, and Text Coach surfaces. Conversation memory tracks names, interests, promises, and objections; background audio keeps coaching running with the screen locked, and the app surfaces mic and server health honestly instead of pretending everything is fine. Apple and Google Sign In, PDF transcript export, OTA updates, and Sentry monitoring round out the platform.
React Native
Expo
Zustand
Node
Express
WebSocket
Claude AI
Deepgram
PostgreSQL
RevenueCat
IN DEV
// op_014
 EDD Paid Family Leave
An independent UX audit and redesign proposal for California EDD's Paid Family Leave claim journey — the path a new parent walks from “I just had a baby” to a first benefit payment. Thirteen findings, every one verified against the live site rather than asserted, two of them severe enough to cost a claimant benefits they are legally entitled to: one page tells care claimants to upload two forms and then tells them further down that those forms cannot be uploaded, and a link labelled for Paid Family Leave resolves to the Disability Insurance page. Nielsen–Molich heuristic evaluation, WCAG 2.1 AA conformance review, automated DOM and contrast analysis (6.57:1 passes AA, 228 of 228 links carry accessible names, 18 of 18 process panels ship collapsed), and readability scoring across five formulas over 1,122 words. Journey-mapped against the 41-day statutory filing deadline, where two of the three parties who must act have no account, no reminder, and no deadline they can see. Ships with two wireframes addressing eight of the thirteen findings and the analysis scripts that produced every number.
Heuristic Eval
WCAG 2.1 AA
Journey Mapping
Readability
Wireframes
Python
WORK SAMPLE
// op_015
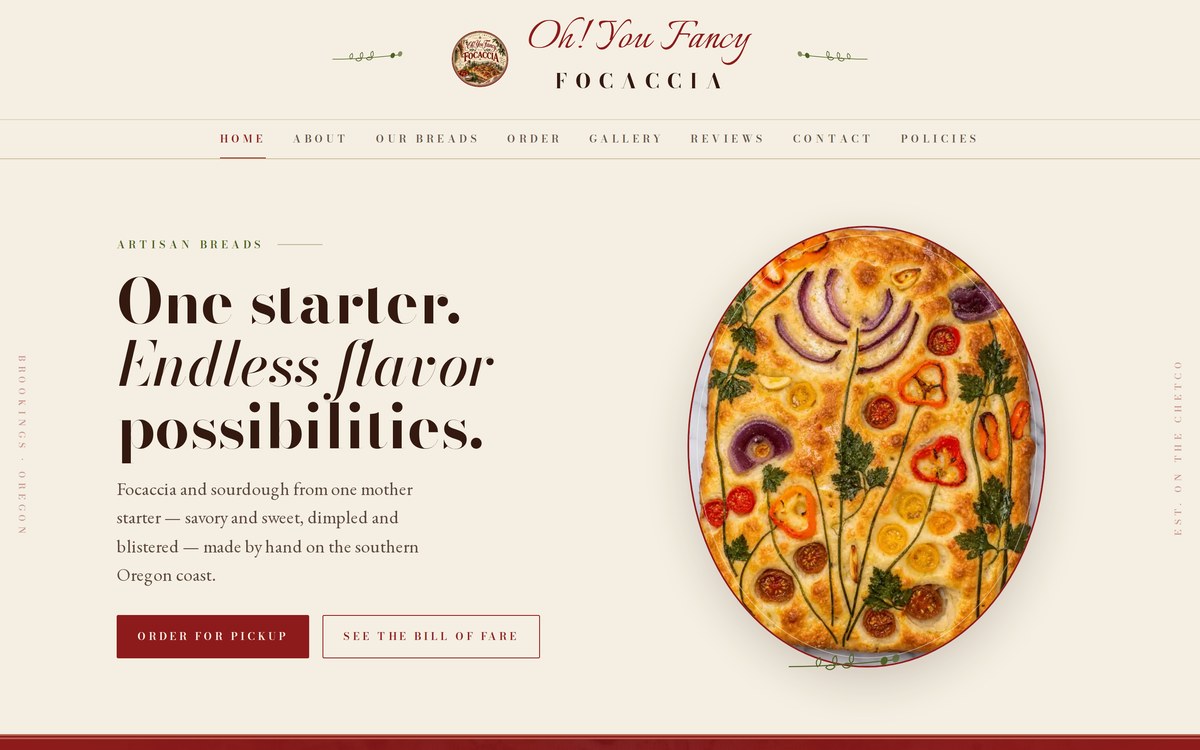 Oh! You Fancy Focaccia
An artisan focaccia and sourdough bakery on the southern Oregon coast, taking orders for market pickup, local delivery and shipping. The customer-facing pages are generated from a single design source and served as plain HTML with no runtime build, so the site ships a Content-Security-Policy with no unsafe-inline — every script is its own file. Behind them, a Node/Express order book on PostgreSQL: a thirty-three bake catalog held in one file that the page generator, the database seed and the test suite all read, so the menu, the bill of fare and the order form cannot drift apart. The order form validates the requested date server-side against the market days, a configurable notice window and the baker’s own vacation blocks. Order lines snapshot the price they were bought at, so repricing the menu never rewrites an order already placed. Transactional email through Resend covers the thank-you, the confirmation and payment receipts, with a tokenised respond link so the baker can accept from her inbox. Schema-change migrations are one-shot and marker-guarded rather than tooled, so a fresh database and a year-old one boot identically — and a value the owner has edited herself is never overwritten on restart. An Expo companion app puts the same order book on her phone for the market table. 102 tests run against a real Postgres in CI.
Node
Express
PostgreSQL
Expo
Resend
Railway
Cloudflare
LIVE
what clients say